P7S Signer and P7S Viewer User Manual
Sign documents of any type in the CAdES / P7S format, create eIDAS electronic signatures (including qualified signatures on a QSCD), and check signed files with P7S Viewer. No technical knowledge needed; developers find PowerShell, C# and VB.NET examples at the end.
1. What are P7S Signer and P7S Viewer?
A file (a contract, an invoice, a report) can be changed by anyone who has it. A digital signature solves two problems:
- Who signed it? The signature is created with your personal digital certificate, so it proves your identity.
- Was it changed? If even one character of the document is modified after signing, the signature is reported as not valid.
P7S Signer signs documents of any type (PDF, Word, images, XML, archives...) in the CAdES format (CMS Advanced Electronic Signatures, ETSI EN 319 122-1) and in the PKCS#7 / CMS format. You can sign a single document, or select an input folder and an output folder and sign hundreds of documents at once (bulk signing). The same signatures can be created automatically, without any window, from the command line (section 13).
The CAdES signatures are the signatures that the eIDAS Regulation (EU) No 910/2014 uses for advanced and qualified electronic signatures on any kind of file. When they are created with a qualified certificate stored on a QSCD (a qualified signature creation device, such as a smart card or a USB token), the result is a qualified electronic signature, which can be checked with the validation tool of the European Commission. Section 7 explains this in detail.
The product has two programs:
| Program | What it does |
|---|---|
| P7S Signer | Signs one document or a whole folder of documents of any type. The result is a signature file with the extension .p7s, .p7m or .cms. Works from the window or from the command line. |
| P7S Viewer | Opens a signed file and tells you who signed it, when, and whether the signature is still valid. It can also give you back the original document, and extract the documents of a whole folder of signed files. |
The signed result is a new file, for example contract-001.pdf.p7s. By default it contains your document and its signature. You can also keep the signature in a separate file (section 8). Your original file is never touched.
Who is this manual for?
- Users — sections 1 to 15 explain, step by step, how to install the product, register it, choose a certificate, sign documents and check them.
- Developers and administrators — sections 16 to 18 explain that P7S Signer is built on the Signature Library (SignLib), and show how to create and verify the same CAdES signatures from Windows PowerShell, C# or VB.NET. One of the purposes of P7S Signer is to let you see what the library can do before you write a single line of code.
Useful links
| What | Address |
|---|---|
| P7S Signer product page (information, purchase, download) | https://www.signfiles.com/p7s-signer/ |
| Signature Library (SignLib) used by P7S Signer | https://www.signfiles.com/signature-library/ |
| CAdES code samples: sign, verify, batch | cades-digital-signature, verify-cades-signatures, batch-cades-digital-signature |
| European Commission validation tool (DSS) | ec.europa.eu/digital-building-blocks/DSS/webapp-demo/validation |
| Support and contact | https://www.signfiles.com/contact/ |
2. Product installation
We recommend installing the product with an Administrator account. After the setup file is verified, the operating system might ask for your permission to install the program: click Yes.
What you need
- Windows 8 or later (including Windows 10, Windows 11 and Windows Server 2022).
- Microsoft .NET Framework 4.6.2 or newer. It is already part of Windows 10 and Windows 11.
- A digital certificate to sign with. If you do not have one yet, you can create a test certificate (section 10).
Installation steps
- Download the setup file. Get
P7SSigner.msifrom the product page and run it. - If Windows SmartScreen appears, allow the program to run. You may see the window Windows protected your PC. Click More info and then Run anyway. See the explanation below.
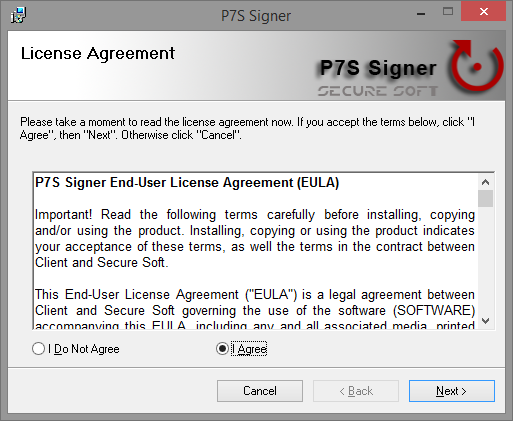
- Read the license agreement. Read the EULA (End-User License Agreement). If you want to continue, select I Agree and click Next.
- Select the installation folder. Keep the proposed folder, or click Browse... to choose another one. Choose Everyone to install the program for all the users of the computer, or Just me for your account only. Click Next.
- Wait for the setup to finish. When Installation Complete appears, click Close. The program is now installed.
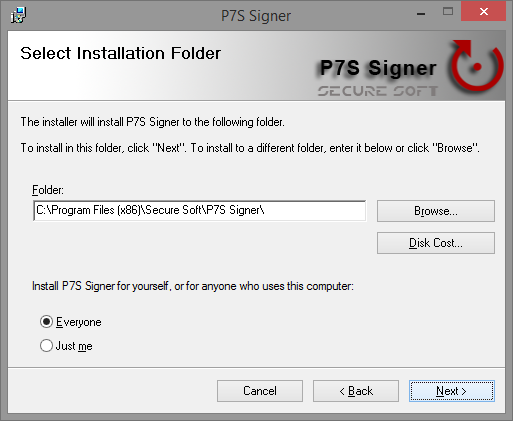
Secure Soft\P7S Signer folder of Program Files (on a 64-bit Windows: C:\Program Files (x86)\Secure Soft\P7S Signer).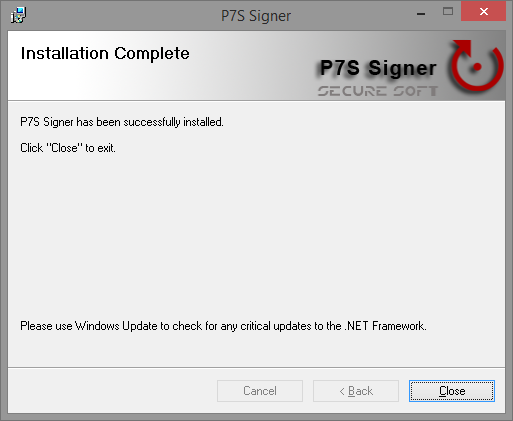
Where to find the programs
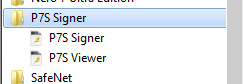
The setup installs P7S Signer and P7S Viewer. The icon of P7S Signer appears on the desktop, and both programs are in the P7S Signer folder of the Windows Start menu.
What is Windows SmartScreen?
SmartScreen is a protection built into Windows. When you run a program you downloaded, Windows compares it with a list of programs that are known and were already downloaded by many people. A program that Windows does not know yet, for example a new version that was published recently, is shown as an unrecognized app, and the window below appears.
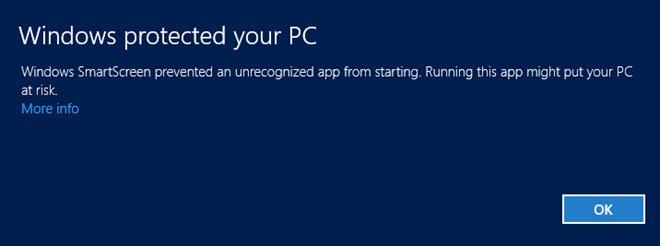
This message does not mean that the file contains a virus. It only means that Windows has no reputation data about it yet. To continue:
- Click More info. The name of the file and of the publisher are displayed.
- Click Run anyway and the setup starts.
Run the setup only if you downloaded it from www.signfiles.com. If you prefer, you can also right-click the downloaded P7SSigner.msi, choose Properties, tick Unblock (at the bottom of the General tab) and click OK. The setup then starts without the SmartScreen message.
3. Trial period and product registration
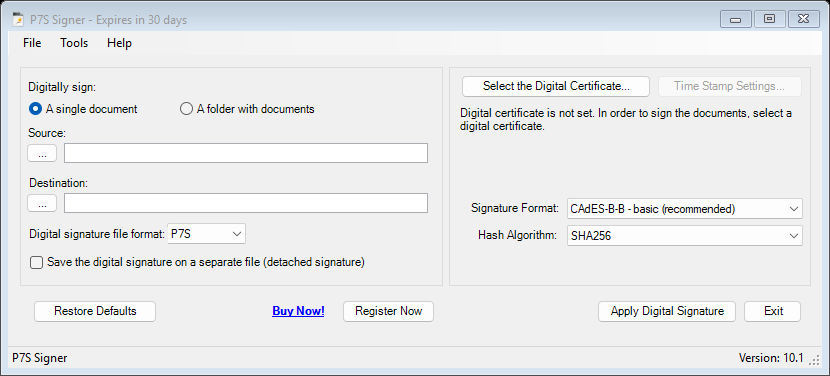
A new, unregistered installation works for a trial period of about 30 days. The title of the window shows how much is left, for example P7S Signer - Expires in 30 days, and the buttons Register Now and Buy Now! are visible.
How to register the product
- Get a serial number. To register the product you need a serial number (also called license code). You can buy it online directly from the product page, https://www.signfiles.com/p7s-signer/. You can also click Buy Now! in the program, which opens the same page.
- Open the registration window. Open P7S Signer and click the Register Now button (or Help → Register Now...).
- Type the license code. Enter the received serial in the first box. The second box, Licensed to (optional), is for a name: if you type one, it is shown in the title of the window.
- Click Register. If the serial number is correct, the product is successfully registered.
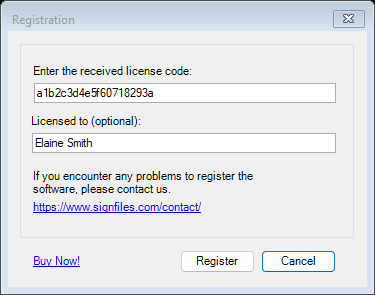
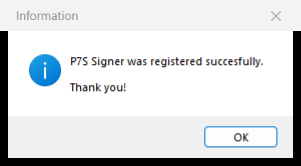
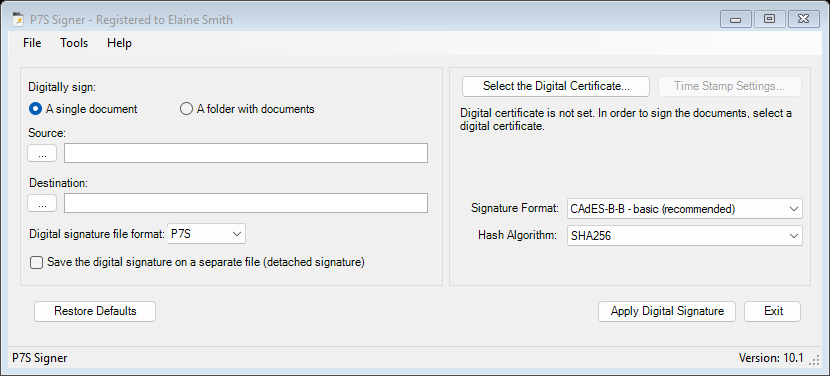
- The license code has 20 characters (letters and digits). Type it exactly as you received it. The messages License code cannot be empty. and Invalid license code. mean that the box is empty, or that the code was mistyped.
- P7S Viewer has its own trial period and its own registration window (Register Now), so register it the same way, with the same license code.
- The registration is saved for the Windows user account that registered the program. If another person uses the same computer with a different account, the registration is done once more with the same code.
When the trial has expired, the title shows Expired on and a date, and the program no longer signs documents (or, for P7S Viewer, no longer opens signed files) until you register.
4. Sign your first document
This is the whole process. It takes less than a minute once you have a certificate.
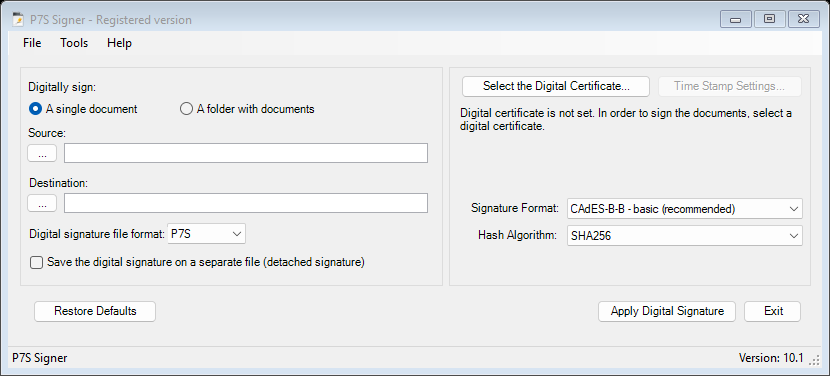
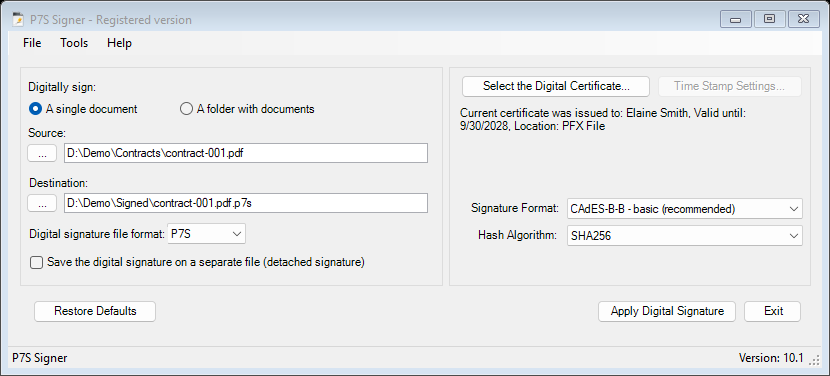
- Choose the document. Keep A single document selected. Click the ... button under Source and select the file you want to sign. The Destination is filled in for you: the same name with
.p7sadded. - Check where to save the signed file. If you want another place or name, click the ... button under Destination. The destination must be a different file from the source.
- Select your digital certificate. Click Select the Digital Certificate.... Choose the certificate from the Windows store, a
.pfxfile or a smart card, and click OK (details in section 6). - Leave the format on the recommended value. CAdES-B-B - basic (recommended) and SHA256 are already selected and are the right choice for most uses (see section 7).
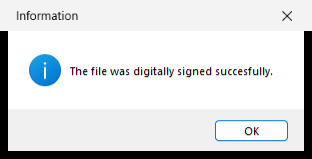
- Click Apply Digital Signature. After a moment you see the message The file was digitally signed succesfully. Your signed file is in the destination you chose.
Drag a document from Windows Explorer and drop it on the P7S Signer window. It is selected as the source automatically, and the destination is proposed.
5. The main window
| Item | What it does |
|---|---|
| Digitally sign | Choose A single document or A folder with documents (all the files of the folder are signed). |
| Source | The document (or folder) you want to sign. Use the ... button to browse. |
| Destination | Where the signed file (or the signed files) will be saved. |
| Digital signature file format | P7S (default), P7M or CMS: the extension of the signed file. See section 8. |
| Save the digital signature on a separate file | Creates a detached signature: the file contains only the signature, not your document. See section 8. |
| Signature Format | The kind of signature to create. The default, CAdES-B-B - basic, is the right choice for normal use. See section 7. |
| Hash Algorithm | The mathematical fingerprint used to detect changes: SHA256 (default), SHA384 or SHA512. Keep SHA256 unless the party receiving your files asks for another one. SHA1 is still in the list for old systems, but it is considered weak: the program warns you when you select it. |
| Select the Digital Certificate... | Opens the certificate window (section 6). Below this button you always see which certificate is currently selected and until when it is valid, and, for the formats that use a time stamp, the time stamp server. |
| Time Stamp Settings... | Available only for the formats that use a time stamp (CAdES-B-T, -LT, -LTA and CAdES-X Long). See section 9. |
| Apply Digital Signature | Signs the document or the folder. While a folder is being signed you can stop it with the Cancel button in the bottom bar; the bar also shows the progress. |
| Restore Defaults | Sets all the options back to their original values (it asks you to confirm first). |
Menus
| Menu | Commands |
|---|---|
| File | Open (choose a document or folder), Apply Digital Signature..., Save Configuration, Save Configuration As..., Load Configuration..., Exit. |
| Tools | Select the Digital Certificate..., Create a self-signed Digital Certificate..., Time Stamp Settings..., Restore Defaults. |
| Help | About... (program version and registration status) and Register Now... (only while the program is not registered). |
6. Digital certificates
A digital certificate is your electronic identity card, issued by a certification authority. To sign with P7S Signer you need one. This section explains where certificates are kept and how to select the one you want to sign with.
6.1 Where the certificates are stored
A certificate that can sign documents has two parts: a public key (the part other people see, inside the certificate) and a private key (the secret part, which only you have). The digital signature is created with the private key. P7S Signer can use certificates from:
- the Windows Certificate Store (called Microsoft Store in the program);
- a PFX (or P12) file;
- a smart card, a USB token or an HSM, through the PKCS#11 interface of the device (6.3).
The Windows Certificate Store (Microsoft Store)
The Windows Certificate Store is the place where Windows keeps the certificates of the computer and of each user. In P7S Signer it appears as Windows Certificate Store and Certificates Available on Microsoft Store.
The certificate store has nothing to do with the Microsoft Store where you download applications. It is only the traditional name of the list of certificates of Windows.
To see the certificates of your account, open the Windows Run window (press Win + R), type certmgr.msc and press Enter:
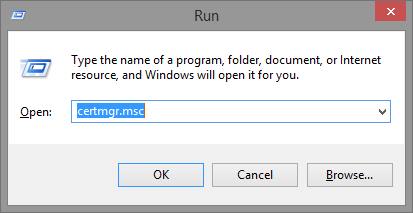
certmgr.msc in the Run window.Then open Personal → Certificates. (The older way still works: Internet Options → Content tab → Certificates button, tab Personal.)
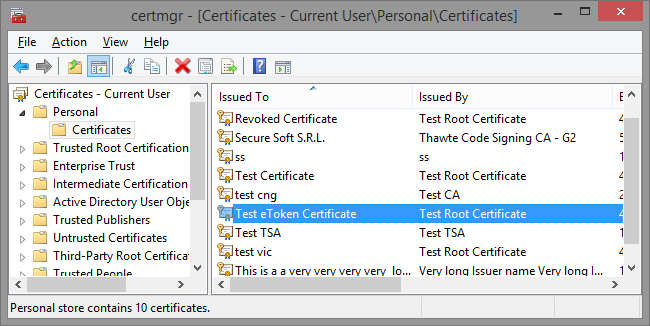
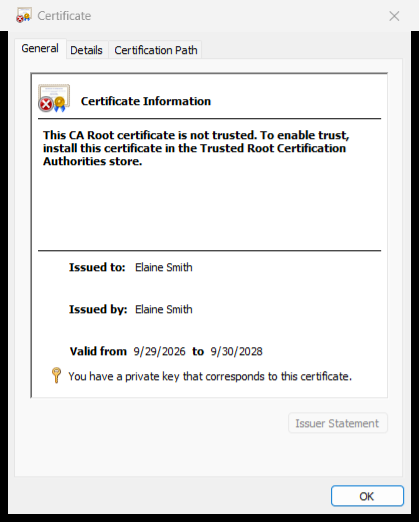
To create digital signatures, the certificates of the Personal store are used. They must have a public and a private key. You can check this by opening a certificate: in the General tab Windows writes You have a private key that corresponds to this certificate.
The private key itself can be stored:
- on the file system of the computer (for example, an imported PFX file);
- on a cryptographic smart card or USB token (like Aladdin eToken or SafeNet iKey) — see 6.2;
- on an HSM (Hardware Security Module), a device that keeps keys for a company.
The certificates you can use are listed per store location: Current User (your own certificates, the usual case) or Local Machine (certificates installed for all the users of the computer).
PFX and P12 files
Another way to keep a digital certificate is a PFX (or P12) file. The file contains the public and the private key of the certificate, and it is protected by a password, to keep the key pair safe.
A PFX/P12 file can be imported into the Windows Certificate Store: just open the file (double-click it) and follow the Certificate Import Wizard. After that, the certificate is available in the Personal list and you can select it from the Windows store without the file.
6.2 Certificates stored on smart cards or USB tokens
If your certificate is stored on a smart card or on a USB token (like Aladdin eToken or SafeNet), the private key never leaves the device: it signs inside the device. This is the kind of device used for qualified certificates (QSCD, see section 7).
P7S Signer can use such a certificate in two ways:
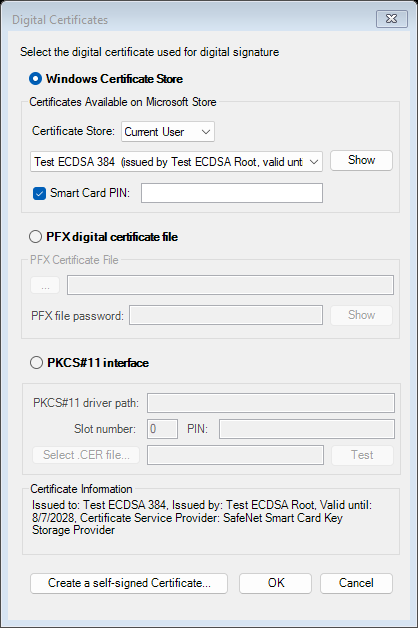
- Through the Windows Certificate Store. The certificate of the device must appear in the store (6.1). When the token is inserted in the USB port, its driver or middleware (the software delivered with the token) usually imports the certificate in the store automatically. If the certificate does not appear in the store, it cannot be used this way: ask your vendor how to add it, and look at the options of the middleware (for example, an option that copies the certificates of the token to the local Windows store).
- Through PKCS#11, directly, with the library of the device (6.3, option C).
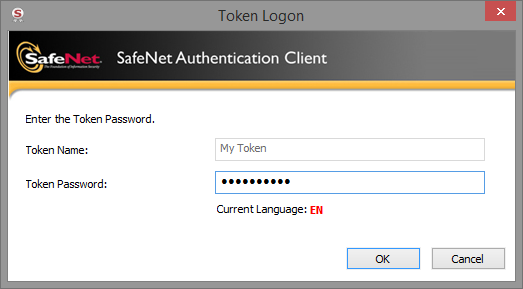
When you sign, the token asks for its PIN. The window belongs to the middleware of the token, for example:
If the token is not connected when you sign, its certificate is not in the list, or the signing ends with an error such as Keyset does not exist. Connect the token and try again.
Normally the PIN is requested every time you sign. If you do not want the PIN window (for example for batch signatures, section 13), tick Smart Card PIN and type the PIN. The PIN is saved encrypted in the configuration, it belongs to the selected certificate, and it is cleared when you select another certificate. If the card rejects the PIN, P7S Signer stops using it (so your card does not get locked by repeated wrong attempts): correct it in this window and try again.
6.3 Select the digital certificate for creating signatures
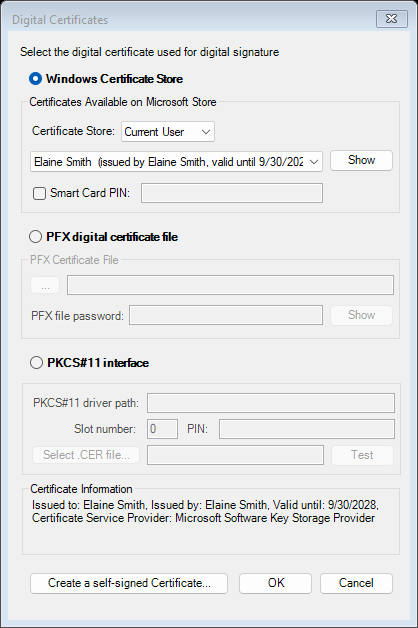
To digitally sign a document, a digital certificate must be selected first. Click Select the Digital Certificate... (or Tools → Select the Digital Certificate...). The certificate can be in a PFX file, in the Windows store or on a PKCS#11 device.
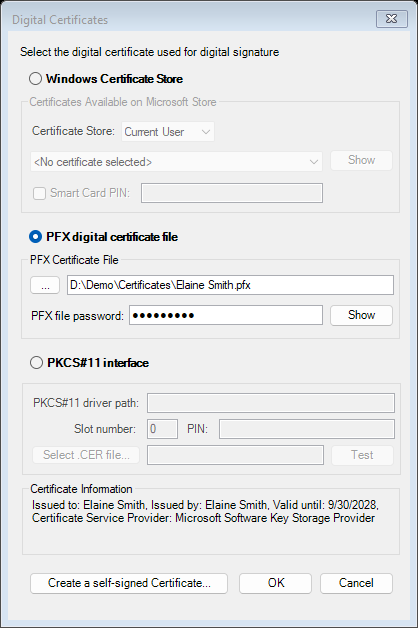
Option A: a PFX file
Some certificates are delivered as a file with the extension .pfx (or .p12), protected by a password.
- Select PFX digital certificate file.
- Click ... and pick your
.pfxfile (or type its path). - Type the PFX file password. The Show button next to it displays the details of the certificate so you can check you picked the right one; the Certificate Information line at the bottom summarizes it.
- Click OK.
Option B: a certificate installed in Windows
Certificates installed on the computer, or stored on a USB token or smart card that Windows knows, appear in the Windows Certificate Store.
- Select Windows Certificate Store.
- In Certificate Store choose Current User (your own certificates, the usual case) or Local Machine (certificates installed for the whole computer).
- Pick your certificate from the list Certificates Available on Microsoft Store. The list shows the name of the owner, the issuer and the expiry date; an expired certificate is marked EXPIRED. Show displays the full certificate.
- If the certificate is on a smart card and you want to avoid the PIN window, tick Smart Card PIN and type the PIN (6.2).
- Click OK.
Option C: a token or HSM through PKCS#11
Tokens, smart cards and hardware security modules come with a PKCS#11 library (a .dll file installed by the manufacturer's software). With this option the program talks to the device directly, without using the Windows store.
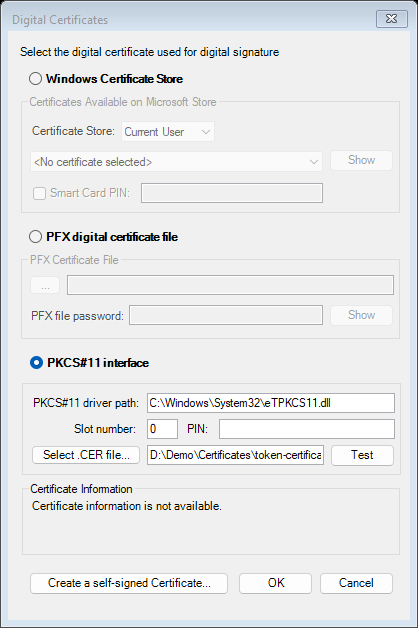
- Select PKCS#11 interface.
- In PKCS#11 driver path pick the library of your device. On a 64-bit Windows use the 64-bit version of the library.
- Type the Slot number (0 is the first device) and the PIN. The PIN cannot be empty.
- Click Select .CER file... and pick the public part of your certificate (a
.ceror.crtfile). The private key stays on the device. - Click Test. The program logs in, finds the key and makes a test signature, so you know everything works before signing. Then click OK.
Certificate Information
At the bottom of the window, Certificate Information summarizes the selected certificate: to whom and by whom it was issued, until when it is valid, and Certificate Service Provider. The last one is the name of the software (or of the device driver) that manages the private key of the certificate. It helps you understand where the key is:
| Provider shown | Where the private key is |
|---|---|
| Microsoft Software Key Storage Provider, Microsoft Enhanced Cryptographic Provider | In your Windows account, on the computer (for example an imported PFX file). |
| eToken Base Cryptographic Provider, SafeNet Smart Card Key Storage Provider or similar names from the token vendor | On a smart card or USB token. A PIN is needed to sign. |
(The abbreviations are CSP, Cryptographic Service Provider, for the classic providers, and KSP, Key Storage Provider, for the newer ones. You do not have to choose them: P7S Signer uses the provider of the certificate.) If the private key is not available on this computer, the line The private key is not available is added.
Both RSA and ECDSA (elliptic curve) certificates are supported, in the Windows store, in PFX files and on PKCS#11 devices. The button Create a self-signed Certificate... at the bottom left is explained in section 10.
If the certificate is expired or not valid yet, or its private key is missing, P7S Signer refuses to sign and explains why. The window warns you already when you select such a certificate. Renew the certificate or choose another one.
7. eIDAS electronic signatures and signature formats
P7S Signer creates the signatures that the European Union uses for electronic signatures on files: CAdES signatures (ETSI EN 319 122-1), stored in a .p7s, .p7m or .cms file. This section explains how they relate to the eIDAS Regulation (EU) No 910/2014, what you need to obtain a qualified electronic signature, which format to choose, and how to check the result with the validation tool of the European Commission.
7.1 The levels of electronic signatures in the eIDAS Regulation
| Level | What it means |
|---|---|
| Electronic signature | Any data in electronic form that the signer uses to sign. It has no special requirements. |
| Advanced electronic signature (AdES) | A signature that is uniquely linked to the signer, identifies the signer, is created with data that the signer keeps under his sole control, and detects any later change of the document (Article 26). CAdES is one of the formats of the advanced signatures. |
| Qualified electronic signature (QES) | An advanced signature that is created by a qualified signature creation device (QSCD) and is based on a qualified certificate issued by a qualified trust service provider. A qualified electronic signature has the equivalent legal effect of a handwritten signature and is recognised in all the Member States (Article 25). |
The same rules apply to electronic seals, which are the signatures of a legal entity, created with a certificate for electronic seals.
7.2 What you need for a qualified electronic signature
The level of a signature is given by the certificate and by the device that holds its private key, not by the software. P7S Signer creates the signature in the CAdES format that the validators expect, and it works with all the kinds of certificates:
| Certificate and private key | Result |
|---|---|
| A qualified certificate whose private key is on a QSCD (a smart card or a USB token, used through the Windows store or through PKCS#11, section 6.2) | A qualified electronic signature (QES). |
| A certificate issued by a certification authority, kept in the Windows store or in a PFX file | An advanced electronic signature, if the certificate identifies the signer and the key is under his sole control. |
| A self-signed certificate (section 10) | A technically correct signature that nobody else trusts. Use it only for tests. |
Qualified certificates are issued by qualified trust service providers, which are listed in the EU Trusted Lists. The provider gives you the certificate on a QSCD, usually a smart card or a USB token. Install the driver of the device, and select the certificate in P7S Signer as explained in section 6.
7.3 Signature formats
The format decides how much information is stored inside the signature. If you are not sure, keep the first one. The four CAdES-B formats are the baseline profiles of ETSI EN 319 122-1, the formats recognised for advanced and qualified signatures.
| Format in the list | What it adds | When to use it |
|---|---|---|
| CAdES-B-B — basic recommended | The signature, the signer's certificate and the signing time. | Everyday use: contracts, invoices, exchanged documents. Works offline and needs no extra settings. |
| CAdES-B-T — with time-stamp | A trusted time stamp from an independent server that proves the exact time of signing. | When you must prove when the document was signed. Needs an Internet connection (see section 9). |
| CAdES-B-LT — long term validation | Time stamp plus the certificates and revocation proofs (OCSP/CRL) of the signer. | Documents that must stay verifiable for years, even after the certificate expires or the issuer's servers are gone. |
| CAdES-B-LTA — long term archival | Everything from LT plus an archive time stamp. | Archives that must remain provable for many years. |
| CMS — old standard | A plain signature in the older PKCS#7 / CMS format, without the CAdES additions. | Only when the receiving software is old and specifically asks for a plain CMS signature. |
| CAdES-C — with references legacy | References to the certificates and to the revocation data of the signer, with their values. | Only for systems that specifically ask for the older CAdES-C format. |
| CAdES-X Long — with time-stamps legacy | CAdES-C plus time stamps of the references. | Only for systems that specifically ask for the older CAdES-X Long format. It needs a time stamp server. |
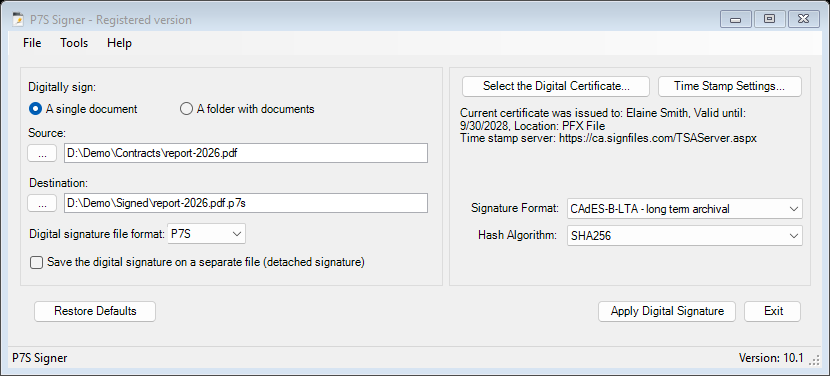
The letters B, T, LT and LTA come from the standard: Basic, Time-stamp, Long Term and Long Term Archival.
The LT and LTA formats store the certificates and the revocation proofs (OCSP responses and CRLs) that are available when you sign. A certificate issued by a certification authority normally has them. A self-signed test certificate has none, so P7S Viewer shows 0 certificates, 0 OCSP responses, 0 CRLs for it.
A time stamp issued by a qualified time stamping service is a qualified electronic time stamp: the date and the time it indicates are presumed accurate (Article 41). If you need this, type the address of a qualified time stamp authority in the time stamp settings.
7.4 Validate the signature with the European validator
The European Commission publishes an open validation tool, DSS (Digital Signature Service, part of the eSignature building block), that checks signatures according to the eIDAS rules. You can use it to confirm that a file created with P7S Signer is a correct CAdES signature and to see its level:
- Open the validation page. Go to ec.europa.eu/digital-building-blocks/DSS/webapp-demo/validation.
- Select the signed file. Choose the
.p7sor.p7mfile created by P7S Signer. For a detached signature, also select the original document in the field for the original documents. - Validate. Keep the default validation policy and start the validation. Read the Simple Report; the Detailed Report and the Diagnostic data explain every check.
The report shows, for each signature:
- the signature format, for example CAdES-BASELINE-B, -T, -LT or -LTA;
- the signer and the certificate chain;
- the signing time or the time of the time stamp;
- the indication of the validation (passed, failed or indeterminate);
- the qualification of the signature. The validator reads the EU Trusted Lists and tells you whether the certificate is qualified and whether its key was on a QSCD. A qualified signature is reported as a qualified electronic signature (QESig).
The result depends on the certificate you used. With a qualified certificate on a QSCD, from a provider listed in the EU Trusted Lists, the validator can report a qualified signature. With a self-signed test certificate, the validator cannot build a trusted chain, so it reports the signature as not trusted (indeterminate), even if the file format is correct. Use the long-term formats (CAdES-B-LT or -LTA) for documents that will be checked years later, because they keep the certificates and the revocation data inside the signature.
The same file can be opened with P7S Viewer (section 14), which checks the signature on your computer and shows the signer, the format and the time stamp, but it does not use the EU Trusted Lists.
8. File format and detached signatures
P7S, P7M or CMS
The three choices of Digital signature file format contain the same kind of data: a signed message in the PKCS#7 / CMS standard. Only the extension differs. Keep P7S unless the party who receives the file expects P7M or CMS. When you change the format, the extension of the proposed destination changes as well.
Detached signature
Normally the signed file contains your document and its signature, so a single file travels. If you tick Save the digital signature on a separate file (detached signature), the signed file contains only the signature. You then keep and send two files: the document and its signature (for example invoice-001.pdf and invoice-001.pdf.p7s).
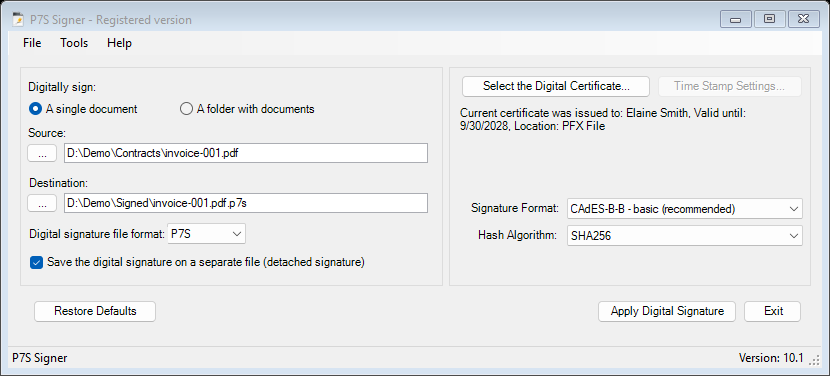
The signature cannot be verified without the document. P7S Viewer looks for the document next to the signature (invoice-001.pdf for invoice-001.pdf.p7s) and asks you to select it when it is not found (section 14).
9. Time stamp settings
A time stamp is issued by a Time Stamp Authority (TSA), an independent service. It proves that your signature existed at a given moment and cannot be back-dated. It is used by CAdES-B-T, -LT, -LTA and CAdES-X Long. Open it with Time Stamp Settings... (also in the Tools menu).
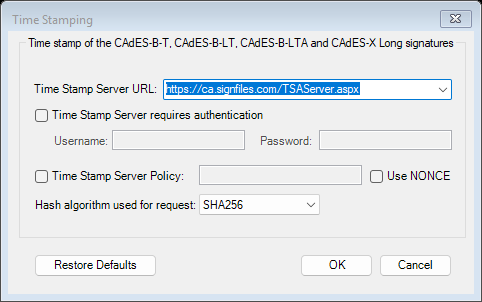
| Setting | Meaning |
|---|---|
| Time Stamp Server URL | The web address of the TSA service. The program starts with https://ca.signfiles.com/TSAServer.aspx. Use the address given by your provider if you have your own. |
| Time Stamp Server requires authentication | Tick it and type the Username and Password if your provider requires them. |
| Time Stamp Server Policy | Tick it only if your provider asked you to send a policy identifier, and type it (it must be a number sequence like 1.2.3.4.5). |
| Use NONCE | A random number that protects the request from being replayed. Tick it if your provider supports it. |
| Hash algorithm used for request | SHA256 by default. |
| Restore Defaults | Puts all these values back to the original ones. |
The computer must be able to reach the time stamp server while signing. If the address is not valid, P7S Signer tells you to set it here before signing. Formats without a time stamp (CAdES-B-B, CMS, CAdES-C) work without any server.
10. Creating a test certificate
If you do not have a certificate yet and only want to try the program, P7S Signer can create a self-signed one. Open Tools → Create a self-signed Digital Certificate... (or the button in the certificate window).
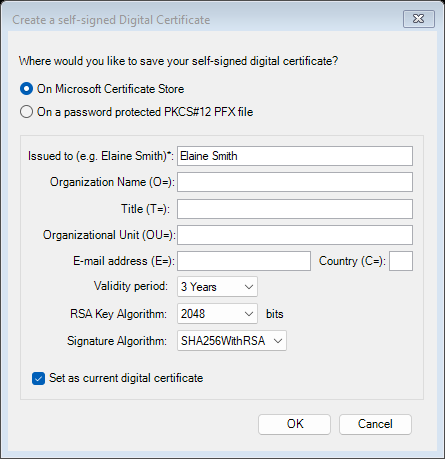
- Choose where to save it: On Microsoft Certificate Store or On a password protected PKCS#12 PFX file (you will be asked for the file name and a password).
- Type Issued to (your name, required) and, if you wish, the organization, unit, title, e-mail address and country code.
- Choose the Validity period (default 3 years), the RSA Key Algorithm length (2048 or 4096 bits, default 2048) and the Signature Algorithm (default SHA256WithRSA). The defaults are fine.
- Keep Set as current digital certificate ticked to use it right away, then click OK.
Nobody except you trusts a self-signed certificate. Other people's programs will show that the signer is unknown. For real documents, use a certificate issued by a recognised certification authority.
11. Signing a whole folder
To sign many documents at once, select A folder with documents.
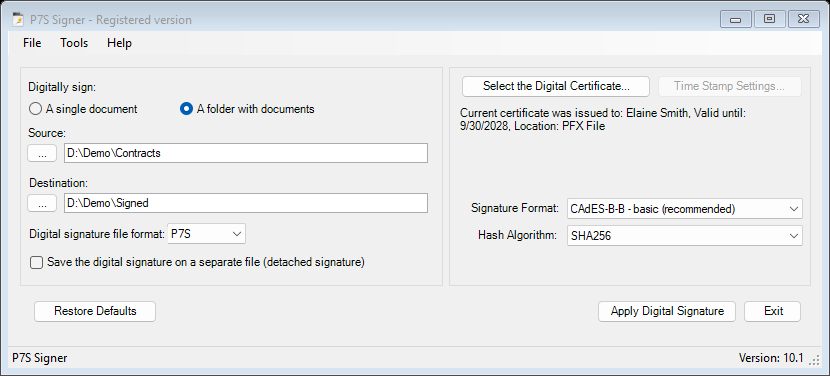
- Under Source choose the folder with your documents.
- Under Destination choose another folder. Every file of the source folder is signed and saved in the destination folder with the same name plus the extension of the signature format:
contract-001.pdfbecomescontract-001.pdf.p7s. The source and the destination must be different folders. - Click Apply Digital Signature. While it works, the bottom bar shows the progress and a Cancel button. When it finishes you see how many documents were signed.
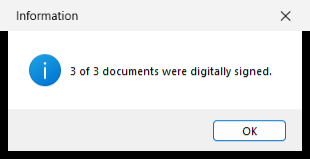
A problem with one file does not stop the others. At the end the message lists the files that failed and why (the first ten). If the PIN of your smart card is rejected, the folder is stopped at once, so the card is not locked by repeated wrong attempts.
If files with the same names already exist in the destination, the program asks you first, or tells you that the destination folder already contains signed documents with the same name. If you pick a destination folder that already contains documents, you are asked whether to use it anyway. If a folder contains no documents you are told: The selected folder does not contain documents.
12. Saving your settings
The program remembers your choices (certificate, format, hash algorithm, time stamp server...) the next time you start it. You can also keep several sets of settings in files — for example one for contracts and one for reports:
- File → Save Configuration As... saves the current settings in a file you name.
- File → Load Configuration... loads them again.
- Tools → Restore Defaults returns everything to the original values.
A saved configuration file is also what the command line uses to sign documents automatically.
A configuration file made by an earlier version is converted automatically (for example, CAdES with the option Time stamp document becomes CAdES-B-T). If a file contains a value that is not valid, the program tells you which one and uses the default value instead. A file that is damaged, or that is not a P7S Signer configuration file, is never used: a damaged current configuration is kept as configuration.xml.bad and the default one is created.
13. Batch signatures (automatically made without user intervention)
P7S Signer can also sign without showing its window, for example from a scheduled task, from a script or from another program. Nobody has to click anything: the program reads the settings from a configuration file, signs, and closes.
By default, P7S Signer is installed in the folder C:\Program Files (x86)\Secure Soft\P7S Signer (on a 32-bit Windows: C:\Program Files\Secure Soft\P7S Signer) and the program is P7S Signer.exe.
Command line parameters
"P7S Signer.exe" <source file> <destination file> [<configuration file>]
"P7S Signer.exe" <source folder> <destination folder> [<configuration file>]- source folder: all the files of the folder are signed, with the same names plus the signature extension (
.p7s,.p7mor.cms), in the destination folder. The destination folder must exist. - configuration file: a file saved with File → Save Configuration As.... When it is not given, the current configuration of the window is used.
- Do not end a path written between quotes with a backslash: write
"C:\Folder", not"C:\Folder\". Windows would read the last backslash and quote as one character and the arguments would be mixed up. - An error on one file of a folder does not stop the other files.
Sign one file
To automatically sign a file, use a command like this one:
c:\Program Files (x86)\Secure Soft\P7S Signer>"P7S Signer.exe" c:\contract.pdf c:\contract.pdf.p7sSign a folder
To automatically sign all the files of a folder:
c:\Program Files (x86)\Secure Soft\P7S Signer>"P7S Signer.exe" c:\InputFolder c:\OutputFolderCustom configuration
In some cases you need a different signature configuration (for example a different certificate, signature format or file format) for different files or folders. To save a specific configuration, open the window, set everything you want, and go to File → Save Configuration As... Save the configuration in a file. Later you can use that file in batch mode to apply a different signature configuration on the signed files.
To automatically sign a folder using a custom configuration:
"P7S Signer.exe" c:\InputFolder c:\OutputFolder c:\config-client2.xmlBecause nobody is there to answer, choose a certificate that does not need any interaction: a PFX file (its password is saved in the configuration, encrypted), a smart card certificate with the Smart Card PIN saved (section 6.2), or a PKCS#11 device (the PIN is saved in the configuration too). The smart card must be connected. The certificate must be valid: an expired certificate stops the signing, with the result code 2.
Result codes
| Code | Meaning |
|---|---|
| 0 | Success. |
| 1 | The signing failed (for a folder: at least one file failed). |
| 2 | The signing could not start: invalid arguments, the source does not exist, the destination is the same as the source, the configuration file is damaged or has values that are not valid, the certificate is not valid, or P7S Signer is not registered. |
The error messages are also written in the command window. P7S Signer is a Windows application, so the command prompt does not wait for it. To wait and read the result code:
cmd:         start "" /wait "P7S Signer.exe" C:\Demo\Contracts C:\Demo\Signed C:\Demo\contracts.config
             echo %errorlevel%

PowerShell: (Start-Process "P7S Signer.exe" -ArgumentList '"C:\Demo\Contracts" "C:\Demo\Signed" "C:\Demo\contracts.config"' -Wait -PassThru).ExitCodeSet up everything once in the window, use Save Configuration As..., and then create a task in the Windows Task Scheduler that starts P7S Signer.exe with the source folder, the destination folder and the configuration file. Use the same Windows account for the task that you used to set up the certificate and the registration.
The reverse operation, extracting the original documents from a folder of signed files, is also available from the command line: see section 15.
14. P7S Viewer
P7S Viewer is the second program of the product. Use it to check a signed file you created or received.
Opening a file
Start P7S Viewer, click ... next to Source file and pick the signed file (.p7s, .p7m or .cms; the list also offers All files). You can also start the program with the file as argument, for example "P7S Viewer.exe" "C:\Demo\Signed\contract-001.pdf.p7s".
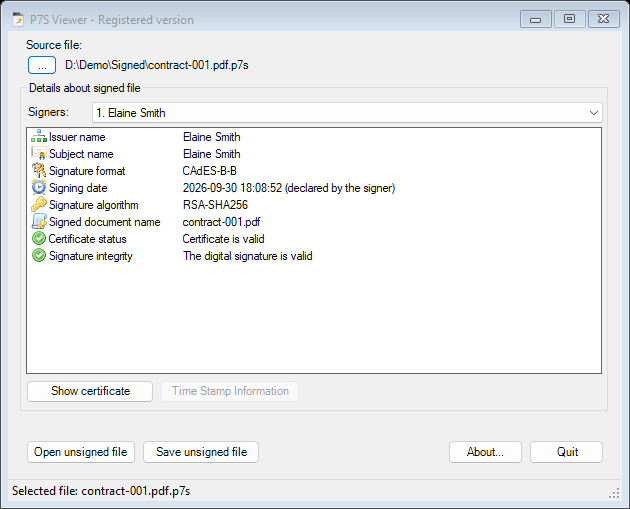
What you see
| Line | Meaning |
|---|---|
| Signers list | Every person who signed the file, numbered. Choose one to see the details below. A file can be signed by several people. |
| Issuer name | The certification authority that issued the signer's certificate. |
| Subject name | The owner of the certificate, that is, the signer. |
| Signature format | For example CAdES-B-B (see section 7). |
| Signing date | When the file was signed. The note (declared by the signer) means it comes from the signer's own computer clock. A trusted time appears only when the signature has a time stamp. |
| Signature algorithm | The technique used, for example RSA-SHA256 or ECDSA-SHA384. |
| Signed document name | The name of the signed document. It is used as the proposed name when you open or save the unsigned file. |
| Certificate status | Certificate is valid, or Certificate is not valid with the reason (expired on a date, or valid only from a date). If the certificate expired but the signature has a time stamp made while it was valid, the line says so. |
| Signature integrity | The most important line. The digital signature is valid means the document is exactly as it was when signed. The digital signature is not valid means it was changed or the signature is damaged. |
| Signature time stamp, Archive time stamps, Validation data | Shown for the T, LT and LTA formats: who issued the time stamp and whether it matches the signature, how many archive time stamps there are, and how many certificates and OCSP/CRL proofs are stored inside. |
| Counter-signatures | Shown when somebody signed the signature itself. They are counted, not verified. |
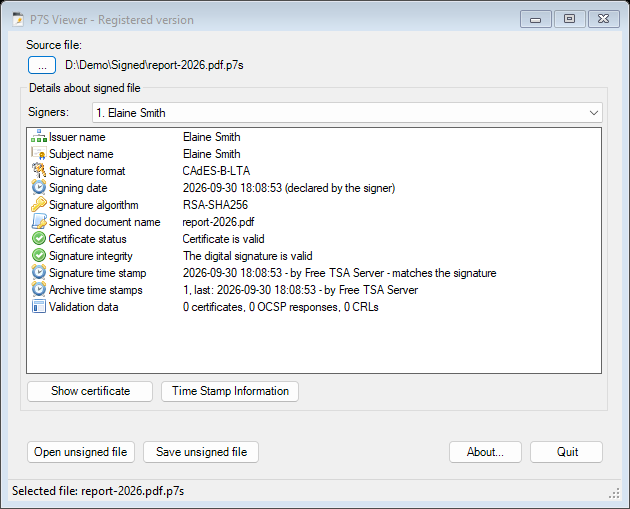
A document that was changed
If somebody changes the document after it was signed, the Viewer says so clearly, and the buttons that give you the unsigned document are disabled:
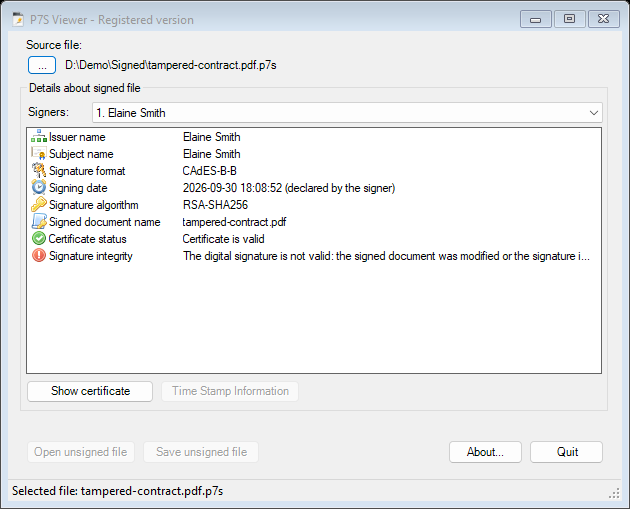
Ask the sender for the original signed file.
Detached signatures
A detached signature contains no document. The Viewer looks for the document next to it (invoice-001.pdf for invoice-001.pdf.p7s). If it does not find it, it tells you and asks you to select the document.
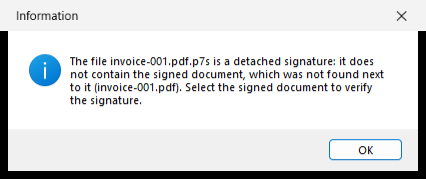
Buttons
- Show certificate — opens the Windows certificate window for the selected signer, with all its details.
- Time Stamp Information — shows the details of the time stamp of the selected signature (only when it has one).
- Open unsigned file — opens a copy of the document, without the signature, in the program associated with its type. If the document is a program or a script (for example
.exe,.bat,.js,.ps1), the Viewer first asks you to confirm, because opening it would run it. - Save unsigned file — saves a copy of the document without the signature.
- About... and Quit.
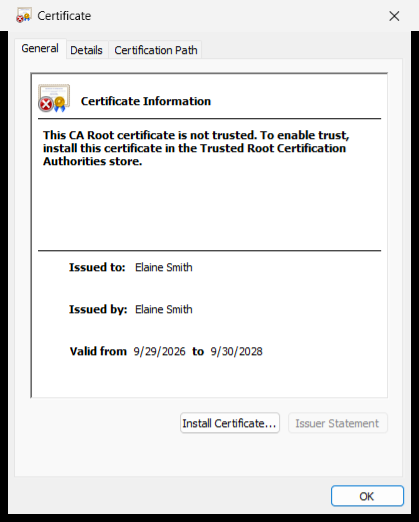
The Viewer checks that the document was not changed and that the certificate is valid. Whether you trust the signer is your decision: check the Issuer name and the Subject name. A self-signed test certificate shows the same name for both.
15. Extracting the documents from many signed files
P7S Viewer can also work without a window, on a whole folder of signed files. It checks the signature of every file and saves the original document in another folder. Use it, for example, to receive many signed documents and get the plain files back.
"P7S Viewer.exe" unsign <source folder> <destination folder>- All the
.p7s,.p7mand.cmsfiles of the source folder are processed (other files are ignored).contract-001.pdf.p7sgivescontract-001.pdfin the destination folder. - A detached signature is verified with its document, which must be next to it in the source folder; the document is copied to the destination.
- An expired certificate is not an error: the document is extracted and the program only notes that the certificate has expired.
- The files that cannot be used — not a PKCS#7 signature, an invalid signature (the document was changed), a detached signature without its document — are copied to the folder
errors, created inside the destination folder, and every problem is written toerrors\errors.log. Your source folder is never changed. - When two signed files would give the same name, the second one is saved as
name (2).pdf.
This is the result on the demonstration folder (the last file was changed after signing):
OK     contract-001.pdf.p7s -> contract-001.pdf
OK     invoice-001.pdf.p7s -> invoice-001.pdf (detached signature, verified with invoice-001.pdf)
OK     old-contract.pdf.p7s -> old-contract.pdf
OK     quarterly-report.pdf.p7s -> quarterly-report.pdf
OK     report-2026.pdf.p7s -> report-2026.pdf
ERROR  tampered-contract.pdf.p7s: The digital signature is not valid: the signed document was modified or the signature is damaged.

Signed files: 6, original documents saved: 5, errors: 1.
The files with errors were copied to D:\Demo\Documents\errors and the errors were written to D:\Demo\Documents\errors\errors.log.| Code | Meaning |
|---|---|
| 0 | All the files were processed (also when the folder contains no signed files). |
| 1 | At least one file could not be verified or saved: see the errors folder. |
| 2 | The command could not start: wrong arguments, the source folder does not exist, the destination is the same as the source, or P7S Viewer is not registered. |
Like P7S Signer, P7S Viewer is a Windows application: use start "" /wait or Start-Process -Wait -PassThru as in section 13 to read the result code.
16. The Signature Library behind P7S Signer
P7S Signer is an application built on the Signature Library (SignLib), a library for .NET that creates and verifies digital signatures: PDF (PAdES), CAdES / PKCS#7, XML (XAdES), Office and more. Everything P7S Signer does is available to your own programs and scripts through the library:
- Library page: https://www.signfiles.com/signature-library/
- Download (library, samples and PowerShell scripts): https://www.signfiles.com/sdk/SignatureLibrary.zip
- Code samples: sign in CAdES format, verify CAdES signatures, batch signatures
The library works with Windows PowerShell, C#, VB.NET and ASP.NET, on .NET Framework and on the recent .NET versions, and it supports certificates from PFX files, from the Windows store and from smart cards, USB tokens and HSMs.
P7S Signer is also a demonstration of the library. Before you write any code, use the window to try a signature format, a hash algorithm, a time stamp server or a certificate, and save the result of your test. Every choice you make in the window is one property of the library (see the table below), and the signed file you get is exactly what your code will produce. P7S Viewer shows you how a signature created by your code looks to the people who receive it.
From the window to the code
CAdES and PKCS#7 signatures are created with the class SignLib.Cades.CadesSignature, and verified with SignLib.Cades.CadesVerify. The table shows what each setting of P7S Signer is in the library.
| In P7S Signer | In the library |
|---|---|
| Signature Format: CAdES-B-B, -B-T, -B-LT, -B-LTA, CMS, CAdES-C, CAdES-X Long (section 7.3) | cs.SignatureStandard = CadesSignatureStandard.CadesBes (or Cms, CadesLT, CadesA, CadesC, CadesXL). The time stamp is added when TimeStamping.ServerUrl is set (CAdES-B-T is CadesBes with a time stamp server). |
| Hash Algorithm | cs.HashAlgorithm = HashAlgorithm.SHA256 (or SHA384, SHA512) |
| Save the digital signature on a separate file (detached signature) | cs.IsDetachedSignature = true |
| Digital certificate from a PFX file | DigitalCertificate.LoadCertificate(pfxFile, password) |
| Digital certificate from the Windows store or a smart card | DigitalCertificate.LoadCertificate(...) with a search criterion, or without parameters to show the selection window |
| Smart Card PIN | DigitalCertificate.SmartCardPin = "..." |
| Time Stamp Server URL, user name, password, policy, NONCE, hash (section 9) | cs.TimeStamping.ServerUrl, .UserName, .Password, .PolicyOid, .UseNonce, .HashAlgorithm |
| Apply Digital Signature | cs.ApplyDigitalSignature(inputFile), which returns the bytes of the signed file |
| Create a self-signed certificate (section 10) | the class X509CertificateGenerator |
| P7S Viewer (section 14) | CadesVerify and CadesSignatureInfo |
The library can do more than the window: co-signatures of a file that is already signed, an explicit signature policy, and the verification of the certificates and of the time stamps. They are shown in section 18.
17. Digitally sign P7S Signer files using Windows PowerShell
The main functions of P7S Signer are available in the SignLib library, which you can download from this link: https://www.signfiles.com/sdk/SignatureLibrary.zip
To digitally sign a P7S file using Windows PowerShell, simply download the library above and inspect the Signature Library\PowerShell Scripts folder. The script for CAdES signatures, signInCAdESFormat.ps1, is there. The version below also verifies the result.
The script
Save it as signInCAdESFormat.ps1, in the same folder with SignLib.dll. It creates a test PFX certificate on the fly, signs the file in the CAdES-B-B format (SHA256) and verifies the result.
#digitally sign a file in the CAdES format (P7S), using a PFX certificate created on the fly
#the script can be configured to use an existing PFX file or a certificate loaded from Microsoft Store (smart card certificate)

if ($args.Length -eq 0)
{
    echo "Usage: signInCAdESFormat.ps1 <unsigned file> <signed file>"
}
else
{
    #SignLib.dll must be on the same folder as the script (or write its full path)
    $DllPath = Join-Path $PSScriptRoot 'SignLib.dll'
    [System.Reflection.Assembly]::LoadFrom($DllPath) | Out-Null

    #create a PFX digital certificate
    $generator = new-object -typeName SignLib.Certificates.X509CertificateGenerator("serial number")
    $pFXFilePassword = "tempP@ssword"
    $generator.Subject = "CN=Your Certificate, E=useremail@email.com, O=Organization"
    $generator.Extensions.AddKeyUsage([SignLib.Certificates.CertificateKeyUsage]::DigitalSignature)
    $generator.Extensions.AddEnhancedKeyUsage([SignLib.Certificates.CertificateEnhancedKeyUsage]::DocumentSigning)

    echo "Create the certificate..."
    $certificate = $generator.GenerateCertificate($pFXFilePassword)

    #digitally sign the file in CAdES format (CAdES-B-B, SHA256)
    $sign = new-object -typeName SignLib.Cades.CadesSignature("serial number")
    $sign.DigitalSignatureCertificate = [SignLib.Certificates.DigitalCertificate]::LoadCertificate($certificate, $pFXFilePassword)

    echo "Perform the digital signature..."
    [System.IO.File]::WriteAllBytes($args[1], $sign.ApplyDigitalSignature($args[0]))

    #verify the signature
    $verify = new-object -typeName SignLib.Cades.CadesVerify($args[1], "serial number")
    echo ("Signatures: " + $verify.Signatures.Count)
    echo ("Valid: " + $verify.Signatures[0].SignatureIsValid)
}
How to run it
How to run the Windows PowerShell script from the command line:
powershell -executionPolicy bypass -file d:\signInCAdESFormat.ps1 d:\test.pdf d:\test.pdf.p7sThe result in the window:
Create the certificate...
Perform the digital signature...
Signatures: 1
Valid: True- Replace
"serial number"with the serial number you received for the library. Without it the library works in demonstration mode: it writes This is a demonstration of the digital signature software and waits 10 seconds before every operation. -executionPolicy bypassallows this one script to run without changing the security settings of the computer.- To sign with an existing PFX file, remove the certificate generator and use
[SignLib.Certificates.DigitalCertificate]::LoadCertificate("d:\certificate.pfx", "password"). For a smart card certificate from the Windows store use the methods described in section 18. - For a detached signature, add
$sign.IsDetachedSignature = $truebeforeApplyDigitalSignature. For a qualified signature, use the qualified certificate of your device (section 7).
18. Digitally sign P7S Signer files using C# or VB.NET
The main functions of P7S Signer are available in the SignLib library (download). To digitally sign a file using C# or VB.NET, download the library, add a reference to SignLib.dll in your project, and inspect the sample projects of the package and the code samples: sign, verify, batch.
Files of any type are signed with the class CadesSignature (namespace SignLib.Cades). It creates CAdES and PKCS#7 / CMS signatures, attached or detached, with an optional time stamp and long-term validation data, and it adds a new signature to a file that is already signed (co-signature). The class CadesVerify verifies the signatures and gives you back the original document.
All the examples below use these namespaces. Every example was run with the library to check the result.
using SignLib;                 // HashAlgorithm
using SignLib.Cades;           // CadesSignature, CadesVerify
using SignLib.Certificates;    // DigitalCertificate
using SignLib.Timestamping;    // time stamp settings
18.1 Sign a file and verify the signature
The smallest program: load a certificate from a PFX file, sign, save the signed file and verify it. The signature format is CAdES-B-B (CadesBes) and the hash is SHA256, exactly like the defaults of P7S Signer. ApplyDigitalSignature returns the bytes of the signed file: you choose where to save it and the extension (.p7s, .p7m).
using SignLib;
using SignLib.Cades;
using SignLib.Certificates;

// "serial number" is the serial number of the library
CadesSignature cs = new CadesSignature("serial number");
cs.DigitalSignatureCertificate = DigitalCertificate.LoadCertificate(@"d:\certificate.pfx", "123456");
cs.SignatureStandard = CadesSignatureStandard.CadesBes;
cs.HashAlgorithm = HashAlgorithm.SHA256;

// apply the digital signature: the input file is not changed
byte[] signed = cs.ApplyDigitalSignature("contract.pdf");
File.WriteAllBytes("contract.pdf.p7s", signed);

// verify the signature
CadesVerify cv = new CadesVerify("contract.pdf.p7s", "serial number");
Console.WriteLine("Format: " + cv.SignatureStandard + ", signatures: " + cv.Signatures.Count + ", document: " + cv.DocumentName);
foreach (CadesSignatureInfo csi in cv.Signatures)
{
    Console.WriteLine("Signer: " + csi.SignatureCertificate.GetNameInfo(X509NameType.SimpleName, false));
    Console.WriteLine("Hash: " + csi.HashAlgorithm.FriendlyName);
    Console.WriteLine("Valid: " + csi.SignatureIsValid);
    Console.WriteLine("Time: " + csi.SignatureTime.ToLocalTime());
    Console.WriteLine("Time stamped: " + csi.SignatureIsTimestamped);
}

// the original document, without the signature
File.WriteAllBytes("contract-unsigned.pdf", cv.UnsignedDocument);
The result:
Format: CadesBes, signatures: 1, document: contract.pdf
Signer: Elaine Smith
Hash: sha256
Valid: True
Time: 9/30/2026 9:24:40 PM
Time stamped: False(X509NameType is in the namespace System.Security.Cryptography.X509Certificates.) The same example in VB.NET:
Imports SignLib
Imports SignLib.Cades
Imports SignLib.Certificates

Module Module1
    Sub Main()
        Dim cs As New CadesSignature("serial number")
        cs.DigitalSignatureCertificate = DigitalCertificate.LoadCertificate("d:\certificate.pfx", "123456")
        cs.SignatureStandard = CadesSignatureStandard.CadesBes
        cs.HashAlgorithm = HashAlgorithm.SHA256

        'apply the digital signature and save the signed file
        File.WriteAllBytes("contract.pdf.p7s", cs.ApplyDigitalSignature("contract.pdf"))

        Dim cv As New CadesVerify("contract.pdf.p7s", "serial number")
        Console.WriteLine("Signatures: " & cv.Signatures.Count)
        For Each csi As CadesSignatureInfo In cv.Signatures
            Console.WriteLine("Valid: " & csi.SignatureIsValid)
        Next
    End Sub
End Module
18.2 Signature levels, time stamp and long-term validation
The format is chosen with SignatureStandard, and the signature is time stamped (CAdES-B-T) when you set the address of a time stamp server (section 9):
| Format in P7S Signer | In the library |
|---|---|
| CAdES-B-B | CadesSignatureStandard.CadesBes, without a time stamp server |
| CAdES-B-T | CadesSignatureStandard.CadesBes and TimeStamping.ServerUrl |
| CAdES-B-LT | CadesSignatureStandard.CadesLT and TimeStamping.ServerUrl |
| CAdES-B-LTA | CadesSignatureStandard.CadesA and TimeStamping.ServerUrl |
| CMS | CadesSignatureStandard.Cms |
| CAdES-C, CAdES-X Long | CadesSignatureStandard.CadesC, CadesSignatureStandard.CadesXL |
CadesSignature cs = new CadesSignature("serial number");
cs.DigitalSignatureCertificate = DigitalCertificate.LoadCertificate(@"d:\certificate.pfx", "123456");

cs.HashAlgorithm = HashAlgorithm.SHA384;                              // SHA256 (default), SHA384 or SHA512
cs.SignatureStandard = CadesSignatureStandard.CadesLT;                // CAdES-B-LT: time stamp + certificates and revocation data
cs.TimeStamping.ServerUrl = new Uri("https://ca.signfiles.com/TSAServer.aspx");
cs.TimeStamping.UseNonce = true;                                      // a random number that protects the request
cs.TimeStamping.HashAlgorithm = HashAlgorithm.SHA256;                 // the hash of the time stamp request
// cs.TimeStamping.UserName = "user"; cs.TimeStamping.Password = "password";   // only if the server requires authentication

File.WriteAllBytes("contract-lt.pdf.p7s", cs.ApplyDigitalSignature("contract.pdf"));

CadesVerify cv = new CadesVerify("contract-lt.pdf.p7s", "serial number");
CadesSignatureInfo csi = cv.Signatures[0];
Console.WriteLine("Format: " + cv.SignatureStandard);
Console.WriteLine("Time stamped: " + csi.SignatureIsTimestamped);
Console.WriteLine("TSA: " + csi.TimestampInfo.TsaCertificate.GetNameInfo(X509NameType.SimpleName, false));
Console.WriteLine("Time stamp altered: " + csi.TimestampInfo.IsTimestampAltered);
The same code with CadesSignatureStandard.CadesA creates a CAdES-B-LTA signature, with an archive time stamp. The time stamp server can be a qualified time stamp authority (section 7.3).
18.3 A certificate from the Windows store or a smart card
When the certificate is in the Windows store (for instance, a qualified certificate on a smart card, section 6.2), load it with a search criterion. No window is shown, so the code can run without a user.
CadesSignature cs = new CadesSignature("serial number");

// the first certificate of the current user whose common name (CN) is "Elaine Smith"
// true = only the valid certificates (issued by a trusted authority); false = any certificate, also a self-signed test one
cs.DigitalSignatureCertificate = DigitalCertificate.LoadCertificate(true, DigitalCertificateSearchCriteria.CommonNameCN, "Elaine Smith");

// the PIN of the smart card, to avoid the PIN window. It applies to the next signature, made on this thread
DigitalCertificate.SmartCardPin = "1234";

File.WriteAllBytes("contract.pdf.p7s", cs.ApplyDigitalSignature("contract.pdf"));SmartCardPin is cleared after every signature. When you sign several files, set it again before each call of ApplyDigitalSignature, as in the next example. Some smart cards do not support this feature: in that case the PIN window of the middleware is shown.
Other search criteria are the other fields of the subject (OrganizationO, EmailE...), the thumbprint and the serial number of the certificate. To let the user choose the certificate in a Windows window, call DigitalCertificate.LoadCertificate() without parameters.
18.4 Detached signatures
By default the signed file contains the document and its signature. With a detached signature the file contains only the signature. The original document is needed to verify it.
CadesSignature cs = new CadesSignature("serial number");
cs.DigitalSignatureCertificate = DigitalCertificate.LoadCertificate(@"d:\certificate.pfx", "123456");
cs.IsDetachedSignature = true;

File.WriteAllBytes("invoice.pdf.p7s", cs.ApplyDigitalSignature("invoice.pdf"));

// verify: the signature and the original document
byte[] signature = File.ReadAllBytes("invoice.pdf.p7s");
byte[] original = File.ReadAllBytes("invoice.pdf");
CadesVerify cv = new CadesVerify(signature, original, "serial number");
Console.WriteLine("Valid: " + cv.Signatures[0].SignatureIsValid);      // False if the document was changed
18.5 Sign all the files of a folder
Create the CadesSignature object once, and sign each file of the folder. For a smart card, set the PIN before every signature. A file that fails must not stop the others.
static void SignFolder(string sourceFolder, string destinationFolder)
{
    CadesSignature cs = new CadesSignature("serial number");
    cs.DigitalSignatureCertificate = DigitalCertificate.LoadCertificate(@"d:\certificate.pfx", "123456");
    cs.SignatureStandard = CadesSignatureStandard.CadesBes;

    foreach (string file in Directory.GetFiles(sourceFolder))
    {
        try
        {
            // DigitalCertificate.SmartCardPin = "1234";      // for a smart card: before each signature
            byte[] signed = cs.ApplyDigitalSignature(file);
            File.WriteAllBytes(Path.Combine(destinationFolder, Path.GetFileName(file) + ".p7s"), signed);
        }
        catch (Exception ex)
        {
            Console.WriteLine("Error: " + file + ": " + ex.Message);
        }
    }
}
18.6 Several signatures in the same file (co-signatures)
A file can be signed by several people. To add a signature, give the signed file as the input: the new signature is added and the previous ones stay valid.
CadesSignature first = new CadesSignature("serial number");
first.DigitalSignatureCertificate = DigitalCertificate.LoadCertificate(@"d:\manager.pfx", "123456");
File.WriteAllBytes("contract.pdf.p7s", first.ApplyDigitalSignature("contract.pdf"));

CadesSignature second = new CadesSignature("serial number");
second.DigitalSignatureCertificate = DigitalCertificate.LoadCertificate(@"d:\accountant.pfx", "123456");
File.WriteAllBytes("contract.pdf.p7s", second.ApplyDigitalSignature("contract.pdf.p7s"));    // the input is the signed file

CadesVerify cv = new CadesVerify("contract.pdf.p7s", "serial number");
for (int i = 0; i < cv.Signatures.Count; i++)
    Console.WriteLine("Signature " + (i + 1) + ": " + cv.Signatures[i].SignatureIsValid + ", signer: "
        + cv.Signatures[i].SignatureCertificate.GetNameInfo(X509NameType.SimpleName, false));
The result:
Signatures: 2
Signature 1: True, signer: Elaine Smith
Signature 2: True, signer: Elaine Smith
18.7 Check the certificate of the signer
SignatureIsValid tells you that the document was not changed and that the signature matches it. It does not tell you whether you trust the signer. Read the certificate and check it:
CadesVerify cv = new CadesVerify("contract.pdf.p7s", "serial number");
X509Certificate2 certificate = cv.Signatures[0].SignatureCertificate;

Console.WriteLine("Issued by: " + certificate.Issuer);
Console.WriteLine("Expires: " + certificate.NotAfter.ToShortDateString());
Console.WriteLine("Status: " + DigitalCertificate.VerifyDigitalCertificate(certificate, VerificationType.LocalTime));
// other checks: VerificationType.OCSP, VerificationType.CRL (they contact the certification authority)
The result: Status: Valid.
18.8 More options of the signature
// an explicit signature policy: identifier (OID), hash of the policy document, OID of the hash algorithm, address of the policy
cs.SetSignaturePolicyInformation("2.16.76.1.7.1.5.2.3", policyHash, "2.16.840.1.101.3.4.2.1", "https://example.com/policy.html");

// the largest CRL that is included in the long-term formats, in bytes (default: 20 MB)
cs.MaxCrlSize = 5 * 1024 * 1024;
18.9 Good to know
| Situation | What happens |
|---|---|
No valid serial number in new CadesSignature("...") | The library works in demonstration mode: it writes a message and waits 10 seconds before each operation. |
DigitalSignatureCertificate not set | A NullReferenceException is thrown. |
| The file to sign does not exist | A FileNotFoundException is thrown. |
| The signature cannot be created (for example, a wrong PIN) | An exception is thrown. Do not retry with the same PIN: repeated wrong PINs lock the card. |
CadesLT or CadesA without TimeStamping.ServerUrl | No error, but the signature has no time stamp: it contains only the certificates and the revocation data, and it is not a complete CAdES-B-LT or CAdES-B-LTA signature. Always set the address of the time stamp server for CAdES-B-T, -LT and -LTA. |
The code creates the same CAdES signature whatever the certificate is. A qualified electronic signature needs a qualified certificate on a QSCD (section 7): load the certificate of the smart card or of the token as in 18.3, and check the result with the European validator (section 7.4).
19. Problems and solutions
| What you see | What to do |
|---|---|
| Windows protected your PC when you start the setup | Windows SmartScreen does not know the new setup file yet. Click More info and then Run anyway, if you downloaded the file from www.signfiles.com (section 2). |
| Invalid license code. | The serial number has 20 characters. Retype it exactly as you received it, without extra characters (section 3). |
| Digital certificate is not set. In order to add a digital signature, select a digital certificate. | Click Select the Digital Certificate... and choose a certificate (section 6). |
| The certificate of the smart card or USB token is not in the list | Connect the token and check that its middleware is installed. The certificate must be in the Windows Certificate Store: open certmgr.msc and look in Personal. If it is not there, use the options of the middleware that copy or register the certificates in the Windows store, or use the PKCS#11 option (section 6.2). Then open the certificate window again. |
| The signing stops with an error such as Keyset does not exist | The token is not connected, or it was removed. Connect it and sign again. |
| The digital certificate ... expired on ... An expired certificate cannot be used to sign documents. | Choose a valid certificate or renew yours with your provider. |
| The private key of the selected certificate cannot be found. | The certificate on the computer has no key to sign with. Import the full certificate (including the private key), or connect your USB token. |
| PFX digital signature certificate error ... | The PFX password is wrong, or the file is damaged. Retype the password in the certificate window. |
| The PIN was rejected by the smart card or by the PKCS#11 device and it is not used again... | Correct the PIN in the certificate window (and use the Test button for a PKCS#11 device). The program will not keep trying with a wrong PIN, to protect the token. |
| PKCS#11 library not found: ... or The PKCS#11 library ... cannot be loaded | Select the correct library of your device. On a 64-bit Windows you need its 64-bit version, and the manufacturer's software must be installed. |
| The CAdES-T signatures require a time stamp server, but the Time Stamp Server URL is not valid. | Open Time Stamp Settings... and type a valid address (section 9). Also check your Internet connection. (The text names the selected format.) |
| The selected folder does not contain documents. | Pick a folder that contains files. |
| The destination file for the signed document already exists. Would you like to overwrite the existing file? | Click Yes to replace it, or No and choose another file name. |
| The configuration contains values that are not valid ... | The program lists the values and uses the default ones. Check the settings, then save them again (section 12). |
| P7S Signer has expired. Would you like to purchase the registered version...? | The trial period ended. Register with your license code (section 3). |
| The batch command does nothing, or the result code is 2 | Read the message in the command window (section 13). The usual causes: a path that ends with a backslash inside quotes, a destination folder that does not exist, a configuration file that does not exist, an expired certificate, or a program that is not registered. |
| The European validator reports the signature as not trusted (indeterminate) | The certificate is not issued by a trusted provider, for example a self-signed test certificate. Sign with a certificate issued by a certification authority, and with a qualified certificate on a QSCD for a qualified signature (section 7.4). |
| Viewer: The file does not exist | Check the path of the file. |
| Viewer: Invalid or corrupt CAdES/PKCS#7 signed data | The file is not a signed file, or it is damaged. Ask the sender for the signed file again. |
| Viewer: The file ... is a detached signature | The signed document is not next to the signature. Select it when asked, or copy it to the same folder. |
| Viewer: The digital signature is not valid | The document was changed after signing, or the signature is damaged. Get the original signed file again. |
Viewer: This file seems to be an email electronic signature (a file named smime.p7s) | The signature belongs to an e-mail. To see it properly, open the original e-mail in your mail program. |
| Library: the program waits 10 seconds and writes This is a demonstration of the digital signature software | The serial number of the library is missing or not valid. Write the serial number in new CadesSignature("...") (section 18). |
Visit www.signfiles.com or use the contact link shown in the registration window, www.signfiles.com/contact.
20. Glossary
| Term | In plain words |
|---|---|
| Digital signature | An electronic seal added to a document. It shows who signed and that the content was not changed. |
| eIDAS | The Regulation (EU) No 910/2014 on electronic identification and trust services. It defines the electronic signatures, seals and time stamps recognised in the European Union. |
| AdES | Advanced electronic signature: a signature that identifies the signer, is under his sole control and detects any change of the document. |
| QES | Qualified electronic signature: an advanced signature created with a qualified certificate on a QSCD. It has the legal effect of a handwritten signature. |
| QSCD | Qualified signature creation device: a certified device, usually a smart card or a USB token, that keeps the private key and signs inside it. |
| Qualified certificate | A certificate issued by a qualified trust service provider, listed in the EU Trusted Lists. |
| EU Trusted Lists | The lists published by the Member States with the qualified trust service providers and their services. Validators use them to decide whether a certificate is qualified. |
| DSS | The open validation tool of the European Commission (Digital Signature Service), which checks signatures according to the eIDAS rules. |
| Digital certificate | Your electronic identity card, issued by a certification authority. It contains your name and a key used to sign. |
| PFX file | A file (.pfx or .p12, the PKCS#12 format) that holds a certificate and its private key, protected by a password. |
| Windows Certificate Store (Microsoft Store) | The place where Windows keeps the certificates installed on the computer or available from tokens and smart cards. It is not the Microsoft Store of applications. Open it with certmgr.msc. |
| PKCS#11 | The standard way for a program to use the keys of a token, smart card or hardware security module, through the library of the manufacturer. |
| Private key | The secret part of your certificate. Only you should have it. It is what makes a signature yours. |
| Smart card / USB token | A small device that keeps your private key and signs inside it, so the key cannot be copied. It is protected by a PIN. |
| Middleware | The software delivered with a smart card or token (for example SafeNet Authentication Client). It lets Windows and the programs use the device, and usually adds its certificates to the Windows store. |
| HSM | Hardware Security Module: a device that keeps the keys of a company and signs on request. |
| CSP / KSP | Cryptographic Service Provider / Key Storage Provider: the component that manages the private key. Certificate Service Provider in P7S Signer shows its name. |
| Windows SmartScreen | A protection of Windows that warns you about programs it does not know yet. A warning does not mean that the program is infected. |
| Hash (SHA256) | A short fingerprint of the document. If the document changes, the fingerprint changes. |
| PKCS#7 / CMS | The general standard for signed messages. The files .p7s, .p7m and .cms use it. |
| CAdES | The European standard (ETSI EN 319 122-1) that extends CMS signatures with signing time, signer information, time stamps and long-term validation data. |
| Detached signature | A signature saved in its own file, separate from the document it signs. |
| Time stamp / TSA | A proof of time issued by a trusted independent service (Time Stamp Authority). |
| OCSP / CRL | Ways to ask the certification authority whether a certificate was cancelled (revoked). The answers can be stored in the signature. |
| Self-signed certificate | A certificate you create yourself. It works technically but nobody else trusts it. Use it only for tests. |
| Serial number (license code) | The code that registers P7S Signer, received after the purchase. The Signature Library has its own serial number. |
| SignLib (Signature Library) | The .NET library on which P7S Signer is built. It lets programs and PowerShell scripts create and verify the same signatures. |
| Batch signing | Signing many documents in one operation, or automatically, without a user, from the command line. |
21. Warning and disclaimer, trademarks
Every effort has been made to make this manual as complete and accurate as possible, but no warranty or fitness is implied. The information provided is on an “as is” basis. The author shall have neither liability nor responsibility to any person or entity with respect to any loss or damages arising from the information contained in this manual. The information about the eIDAS Regulation is a simplified explanation and it is not legal advice.
.NET, Windows, PowerShell, SmartScreen and Visual Studio are trademarks of Microsoft Corporation. All other trademarks are the property of their respective owners.